Sign-in and user accounts, handled Available
Your app gets sign-in, user accounts, and lifecycle management without you building any of it — backed by AWS Cognito under the hood. Identity stays cleanly separated from permissions: this module answers who is this, the permissions module answers what may they do.
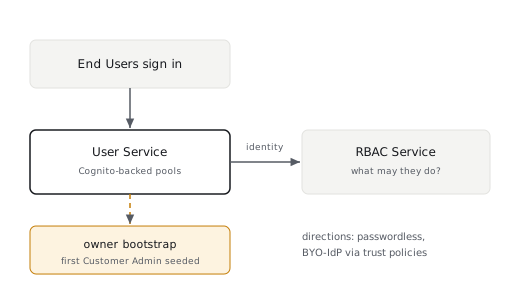
- Owner bootstrap: the first Customer Admin identity is seeded with every Instance.
- Passwordless sign-in as the primary direction for End User auth.
- Planned: bring-your-own IdP via trust policies, keeping RBAC as the authorization layer.